๐Ÿ“‹ GRC compliance for CMMC 2.0, CPCSC, CPA Canada, IIROCโ€ฆSaaS discovery for data governanceFree enriched web chat widget๐Ÿš€ Enriched remote support without your laptop

Run your first compliance assessment

A task guide: the pages to use, in order.
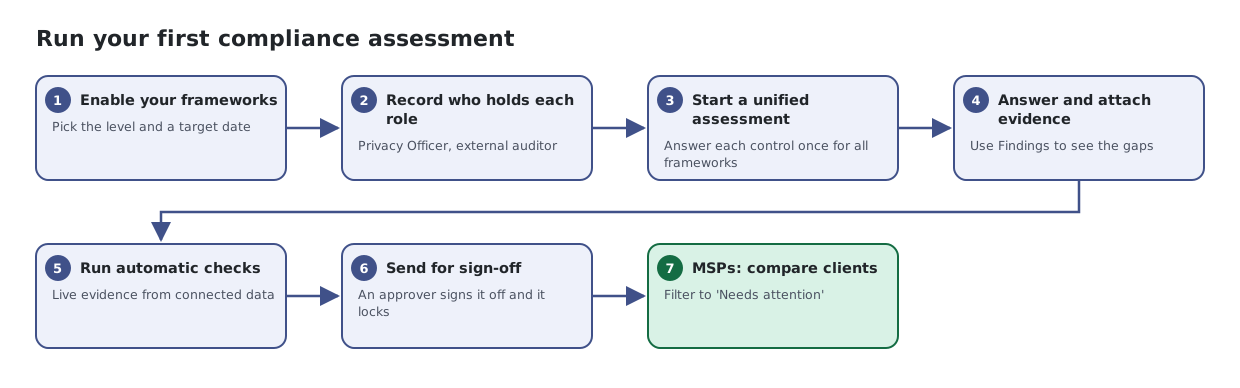
Seven steps: enable a framework, record who holds compliance roles, start a unified assessment, answer questions and attach evidence, run automatic checks for live evidence, send the assessment for sign-off, and, for MSPs, compare clients in the portfolio.
The same steps are listed below, with links to each page's article.

Steps

  1. Enable your frameworks. Pick the level and a target date
  2. Record who holds each role. Privacy Officer, external auditor
  3. Start a unified assessment. Answer each control once for all frameworks
  4. Answer and attach evidence. Use Findings to see the gaps
  5. Run automatic checks. Live evidence from connected data
  6. Send for sign-off. An approver signs it off and it locks
  7. MSPs: compare clients. Filter to 'Needs attention'

Articles for the pages in this guide

← All task guides