Identity & Account Management
See every user account from Active Directory, Microsoft 365, Google Workspace and local computer accounts in one list, with the risks that matter.
What the page is for
Most organizations have the same person in several places: Active Directory, Microsoft 365 and Google Workspace, plus local accounts on their computers. This page merges all of those sources into one table, one row per person, so you can see each account's status, last login, password age, MFA and risk flags together.
Local Windows accounts seen by the Lavawall agent are matched to the right person where the name matches. Built-in accounts such as a local Administrator stay as a separate row for each computer, because each one is a different account.
Clickable summary cards at the top count common risks, such as admins, accounts without MFA, accounts inactive for 90 days or more, passwords that never expire, and failed logins or brute-force attempts. Click a card to filter the list. You can also add contact details and notes to a person and link them to their computers.
What you see
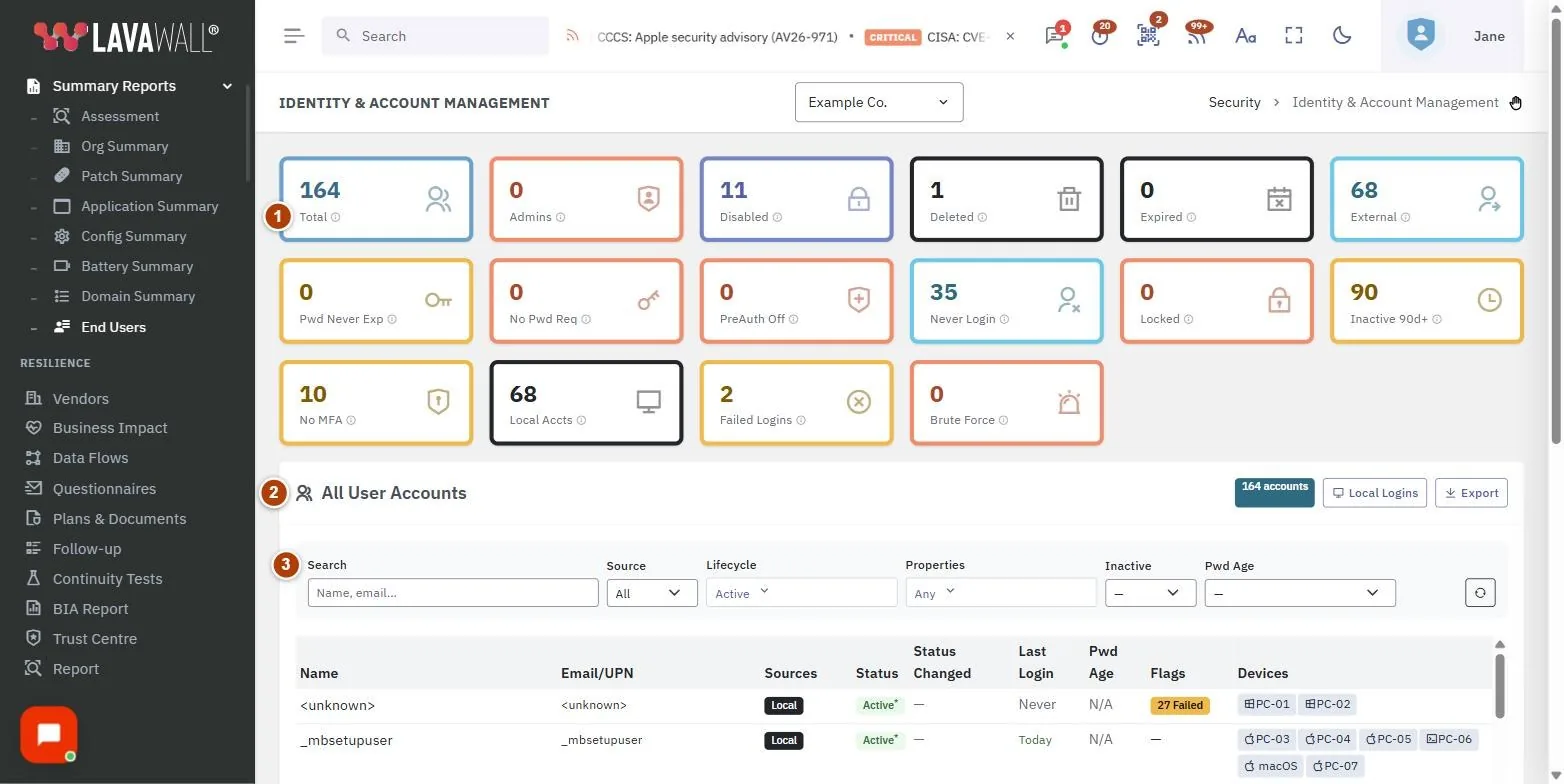
- Summary cards: Total, Admins, Disabled, Deleted, Expired, External, Pwd Never Exp, No Pwd Req, PreAuth Off, Never Login, Locked, Inactive 90d+, No MFA, Local Accts, Failed Logins and Brute Force. Click a card to filter.
- All User Accounts header: the account count, Local Logins and Export.
- Filters: Search, Source (AD, M365, GW, Local), Lifecycle (Active, Disabled, Locked, Expired, Deleted), Properties, Inactive, Pwd Age and a reset button.
- Accounts table: Name, Email/UPN, Sources, Status, Status Changed, Last Login, Pwd Age, Flags and Devices.
- Edit Contact window: First Name, Last Name, Phone, Mobile, City and Notes.
How to find risky accounts
- Click a summary card, for example No MFA or Inactive 90d+. Click it again to clear.
- Or open Properties and tick one or more options, such as Admin, No MFA, Weak MFA, Never Logged In, Pwd Never Expires, Local Admin, Stale Local, Failed Logins or Brute Force.
- Use Inactive (30+d, 90+d, 365+d) and Pwd Age to find old accounts and old passwords.
- Click a column heading to sort, for example Last Login.
How to include disabled or deleted accounts
- Open Lifecycle. Only Active is ticked by default.
- Tick Disabled, Locked, Expired or Deleted, or click All.
- Status Changed shows when Lavawall first saw the account enter its current state.
How to edit a person's contact details
- Hover over the person's name and click the edit button.
- Fill in First Name, Last Name, Phone, Mobile, City and Notes.
- Click Save. A note icon appears beside names that have notes.
How to link a computer to a person
- In the Devices column, click the add button.
- In Assign Device, search for the computer and select it.
- Click Assign.
- To remove a manual assignment, click the ✕ beside the device and confirm. Automatic assignments cannot be removed.
How to export
- Set the filters you want.
- Click Export to download the list.
Tips
- The Sources badges show where each account exists, so you can spot an account that was removed from Microsoft 365 but still exists in Active Directory.
- Local Only accounts exist only on computers and are not in any directory. Check that they are expected.
- Click Local Logins for event-by-event detail of local Windows logons.
- Hover over a summary card for a description of what it counts.
- Manually assigned devices are shown with a dashed outline.
Troubleshooting
- An account appears twice. The sources could not be matched by name. Check the email or user name in each source.
- Failed Logins and Brute Force show a dash. Login events are still loading or no local login data is available for this company.
- "Cannot remove auto assignments." The device was linked automatically from its login history and can only be changed at the source.
Task guides that use this page
Related articles
Still need help?
Search the support centre, or contact our support team and tell us which page you were on.
Names, companies, devices and figures in the pictures are examples. Other product and company names are trademarks of their respective owners.